The public API now requires an API key
SecurityCalling the public REST API (/api/v1/...) now requires an API key, sent as Authorization: Bearer <key>. The previous X-Organization-Id header, which identified an organization without checking any secret, no longer works. A request with a missing, invalid, or revoked key gets a 401.
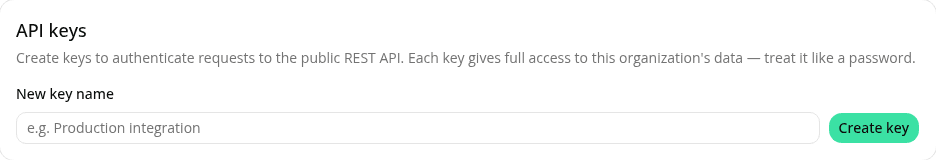
Create and revoke keys from your organization's Settings page in the dashboard. A key is scoped to your organization and grants full access to its data, so treat it like a password: a new key's value is shown once, right after creation, and never again.
This is a breaking change for any script or integration still sending X-Organization-Id: it needs to switch to a bearer key. Every endpoint under /api/v1/, including GET /api/v1/sites, requires a valid key; none stay open.
See Authentication for the full walkthrough.
Resources