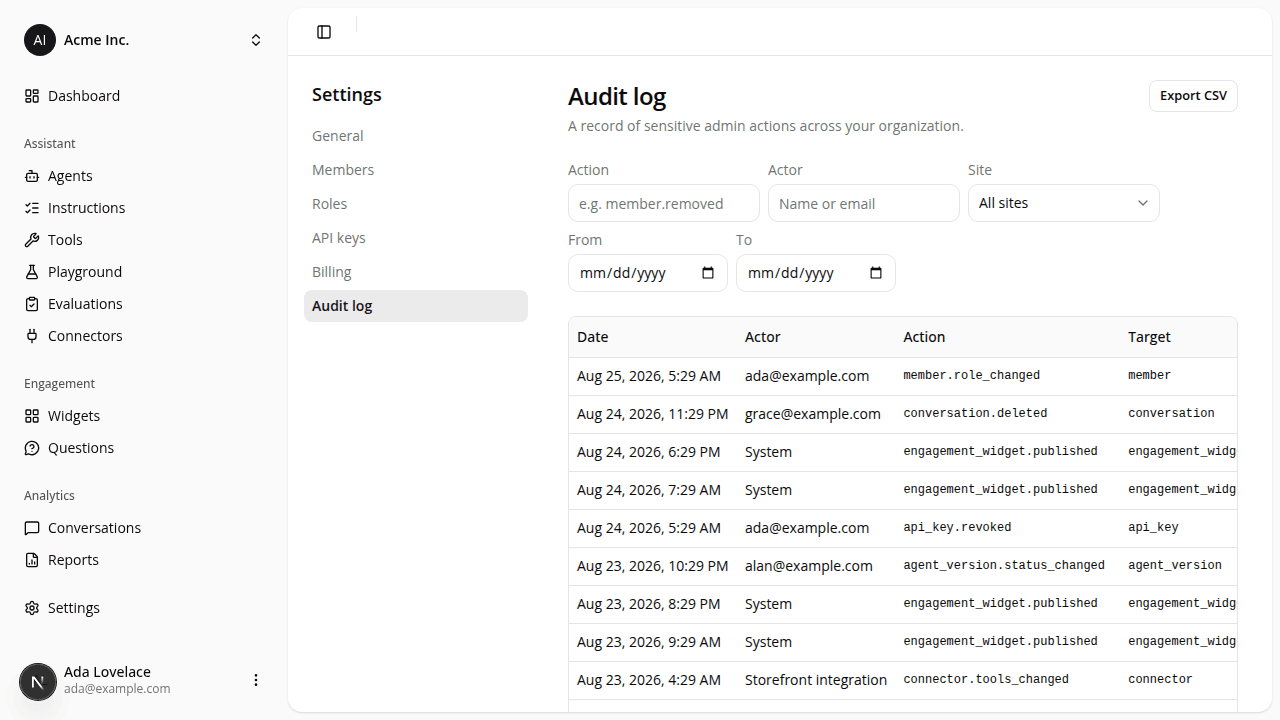
The audit log now covers essentially every admin action
ChangedThe audit log used to record a short list of removals and revocations: a member leaving, a role changing, an API key or invitation revoked, a conversation deleted. Everything else your team did in the dashboard went unrecorded.
It now records nearly every configuration change across your organization: creating, editing, or deleting a site (and every change to its security perimeter: public access, origins, its public key); creating agents and configuration versions and changing a version's status; adding or editing a connector and its enabled tools; instruction blocks; engagement widgets, including publishing, restoring, and minting or revoking a storefront preview link; starter questions; launching an evaluation run or editing a custom scenario; and your organization's profile, roles, and API keys.
Two things are new about how an entry itself is captured, not just how much is covered:
- A blocked attempt is recorded too. If a member tries an action their role doesn't allow, that attempt now writes its own entry naming what they tried, distinct from a genuine successful action.
- Dashboard entries record where they came from: the IP address and browser behind the action, held on the record for investigating a security concern.
The audit log's CSV export also now flags itself when your filters match more rows than the 5,000-row export cap, instead of silently cutting off the rest.
Resources